Emma Doyley
“I find a lot of inspiration in women's rugby and often draw parallels with women in tech and cyber security”
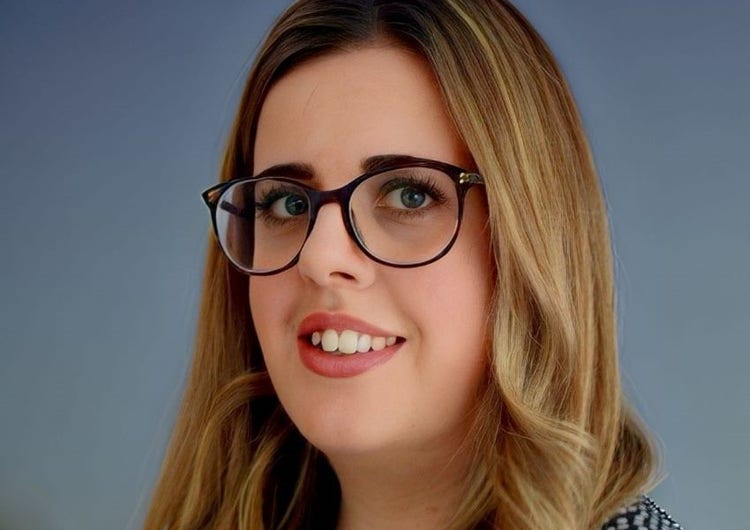
Part of the Tech Women Celebration 50 – a curated list of some of the most inspirational women working at all levels of tech
Emma Doyley is a CISO with a practical, no-nonsense approach to information security. She focuses on understanding real risks, putting sensible controls in place, and making security work for the business rather than against it. She has a strong track record of improving security posture while keeping things clear and manageable for both technical and non-technical teams.
Known for asking the right questions (and not avoiding the difficult ones), Emma works to balance risk, compliance, and day-to-day operations. She's particularly interested in building awareness and engagement, helping people understand their role in keeping systems and data secure.
Tell us about your biggest achievement to date
One of my biggest achievements has been delivering ISO 27001 implementations in very short timeframes, often with a small team or sometimes no dedicated security resource at all.
Rather than treating it as a tick-box exercise, I've always tried to use the framework as a way to make real, practical improvements. I tend to take a pragmatic, risk-based approach - focusing on what matters and making sure controls work in the real world, not just on paper.
A big part of that has been working closely with teams to make requirements feel simpler, more relevant, and easier to adopt in day-to-day work. I've also put a lot of focus on building a security-aware culture, helping people understand why things matter rather than just telling them what to do. The result has been successful certifications alongside a genuine uplift in how security is understood and applied across the business.
What is the most significant challenge you have overcome?
One of the most significant challenges I've overcome was stepping into my first CISO role last year in the middle of a business going through a divestment. It was a period of constant change, with shifting priorities, uncertainty across the organisation, and a lot of moving parts to manage.
Shortly after the separation, we also lost several key team members, which left gaps not only in security but across the wider infrastructure team. This meant I had to quickly grow into the CISO role while also providing support and guidance beyond my immediate remit.
It was a steep learning curve, balancing strategic responsibilities with very hands-on delivery, often at the same time. I had to build relationships quickly, establish credibility, and keep things moving forward despite limited resources.
What I'm most proud of is that we kept momentum, maintained stability, and continued to improve the security posture during a particularly challenging period. It pushed me to adapt quickly, trust my judgement, and lead with a calm, practical approach even when things felt uncertain.
Tell us something about you people would find surprising
I'm a huge rugby fan—especially the Red Roses. I was lucky enough to attend several games at last year's Women's Rugby World Cup, including the final, which was an incredible experience. I am the proud owner of the now traditional red cowboy hat, which makes an appearance at every match!
More seriously, I find a lot of inspiration in women's rugby and often draw parallels with women in tech and cyber security. The visibility, resilience, and teamwork you see on the pitch feel very relevant to the challenges we face in the industry, particularly around representation and breaking down barriers.
I try to bring that perspective into my work where I can, whether that's through mentoring, encouraging others, or just keeping the conversation going.