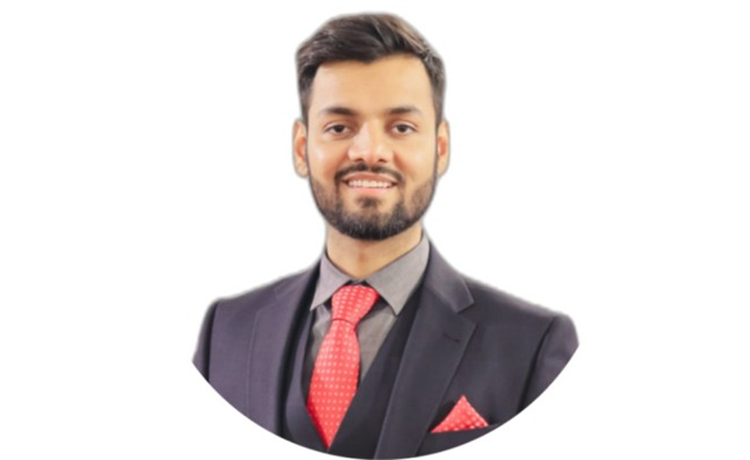
Daniyal Naeem
Part of the IT Leaders 100 - a list of the most influential IT leaders in the UK in 2026.
Daniyal Naeem is Principal Security Authority for AI at BT Group, where he contributes to enterprise-wide security strategy, governance and architecture for AI adoption. Recognised as a Distinguished Engineer, he plays a key role in defining how AI is securely deployed at scale across the business.
Daniyal specialises in securing large-scale AI and agentic systems, bringing a threat-informed perspective grounded in experience across cyber threat research and global incident response. He is a contributor to the MITRE ATT&CK framework and supports ISC2 through exam development.
Daniyal contributes to industry bodies including ETSI and GSMA, helping shape the direction of AI and cybersecurity at an industry level.
What's the most exciting part of your current role?
Shaping how AI is securely adopted at enterprise scale, at a point where industry standards are still evolving. As Principal Security Authority for AI at BT Group, I define security strategy and governance for AI platforms used across a global organisation of over 100,000 people.
This role sits at the intersection of innovation, risk and architecture, where decisions directly influence how safely and confidently the organisation can adopt AI. I work closely with senior leadership to embed security into emerging technologies such as agentic systems, ensuring guardrails are in place before widespread adoption.
What makes this particularly rewarding is enabling innovation at scale, creating frameworks that allow hundreds of teams to build AI solutions securely, without slowing them down.
What do you do in week one of a new project to avoid pain in month six?
I focus on embedding security and governance into the foundation of the project, rather than treating them as downstream concerns. This starts with defining clear principles around identity, data handling, access control and observability to ensure they are part of the architecture from day one.
For AI initiatives, I establish baseline requirements covering agent behaviour, logging, runtime controls and risk boundaries. I also work closely with architects and delivery teams to translate these into practical, implementable designs.
Equally important is early stakeholder alignment. I engage senior stakeholders to define risk appetite and expectations upfront, reducing ambiguity later.
By front-loading these decisions, I minimise rework, avoid late-stage security challenges, and enable teams to move faster with confidence.
What’s the part of your estate you most want to simplify in 2026?
The security and governance model for agentic AI systems. As AI adoption accelerates, complexity grows across identity, orchestration, data access and runtime behaviour.
My focus is on standardising these controls into reusable, platform-level guardrails so teams don't need to solve the same security challenges repeatedly. This includes simplifying how policies are applied, how agents are monitored, and how compliance is demonstrated.
By reducing fragmentation and embedding security into platforms, we can make secure development the default rather than the exception. Simplification here is critical to scale AI safely and enable innovation while maintaining consistent, enterprise-wide control.
Excluding smartphones, what piece of technology could you not live without and why?
My laptop is the one piece of technology I rely on most, as it enables me to operate across both technical depth and strategic influence. It's where I design security architectures, develop governance frameworks, and collaborate with teams and stakeholders across the organisation.
In a role that spans engineering, risk and executive advisory, the ability to rapidly research, analyse and communicate is essential. My laptop effectively acts as a central hub, connecting me to complex systems, global teams and decision-making processes.
More broadly, it represents the flexibility and capability that modern IT provides, allowing me to work seamlessly across domains and contribute meaningfully at both technical and leadership levels.
What excites you most about the future of IT?
The transition towards intelligent, autonomous systems powered by AI. We are moving beyond traditional software into environments where systems can reason, adapt and collaborate.
This fundamentally reshapes the security landscape. Concepts such as identity, trust and control must evolve to support machine-driven interactions at scale, particularly in agentic ecosystems.
I'm excited by the opportunity to help define these emerging security paradigms, embedding governance, observability and resilience into the foundations of AI systems. Organisations that get this right will be able to innovate at pace while maintaining trust.
The future of IT is not just about technological advancement, but about enabling that progress responsibly and securely at scale.
What talent are you quietly proud of that would never show up on LinkedIn?
My ability to translate complex technical concepts into clear, actionable insights for different audiences. In my role, I often bridge deep technical domains and executive decision-making, where clarity is critical.
Whether advising senior leadership on AI risk or supporting engineering teams with security requirements, I focus on making complexity understandable and practical.
This ability has also supported my external speaking, where I regularly deliver keynotes at industry conferences. Engaging diverse audiences and making emerging topics like AI security accessible is something I value, even though it's not always visible as a formal achievement.
What’s your most-used keyboard shortcut or command that you wish everyone knew?
Ctrl + Shift + V (paste without formatting). It's a small but powerful shortcut that saves time and avoids formatting issues when working across multiple tools and environments.
It reflects a broader mindset I value: small efficiencies, when consistently applied, can significantly improve productivity and quality over time!